

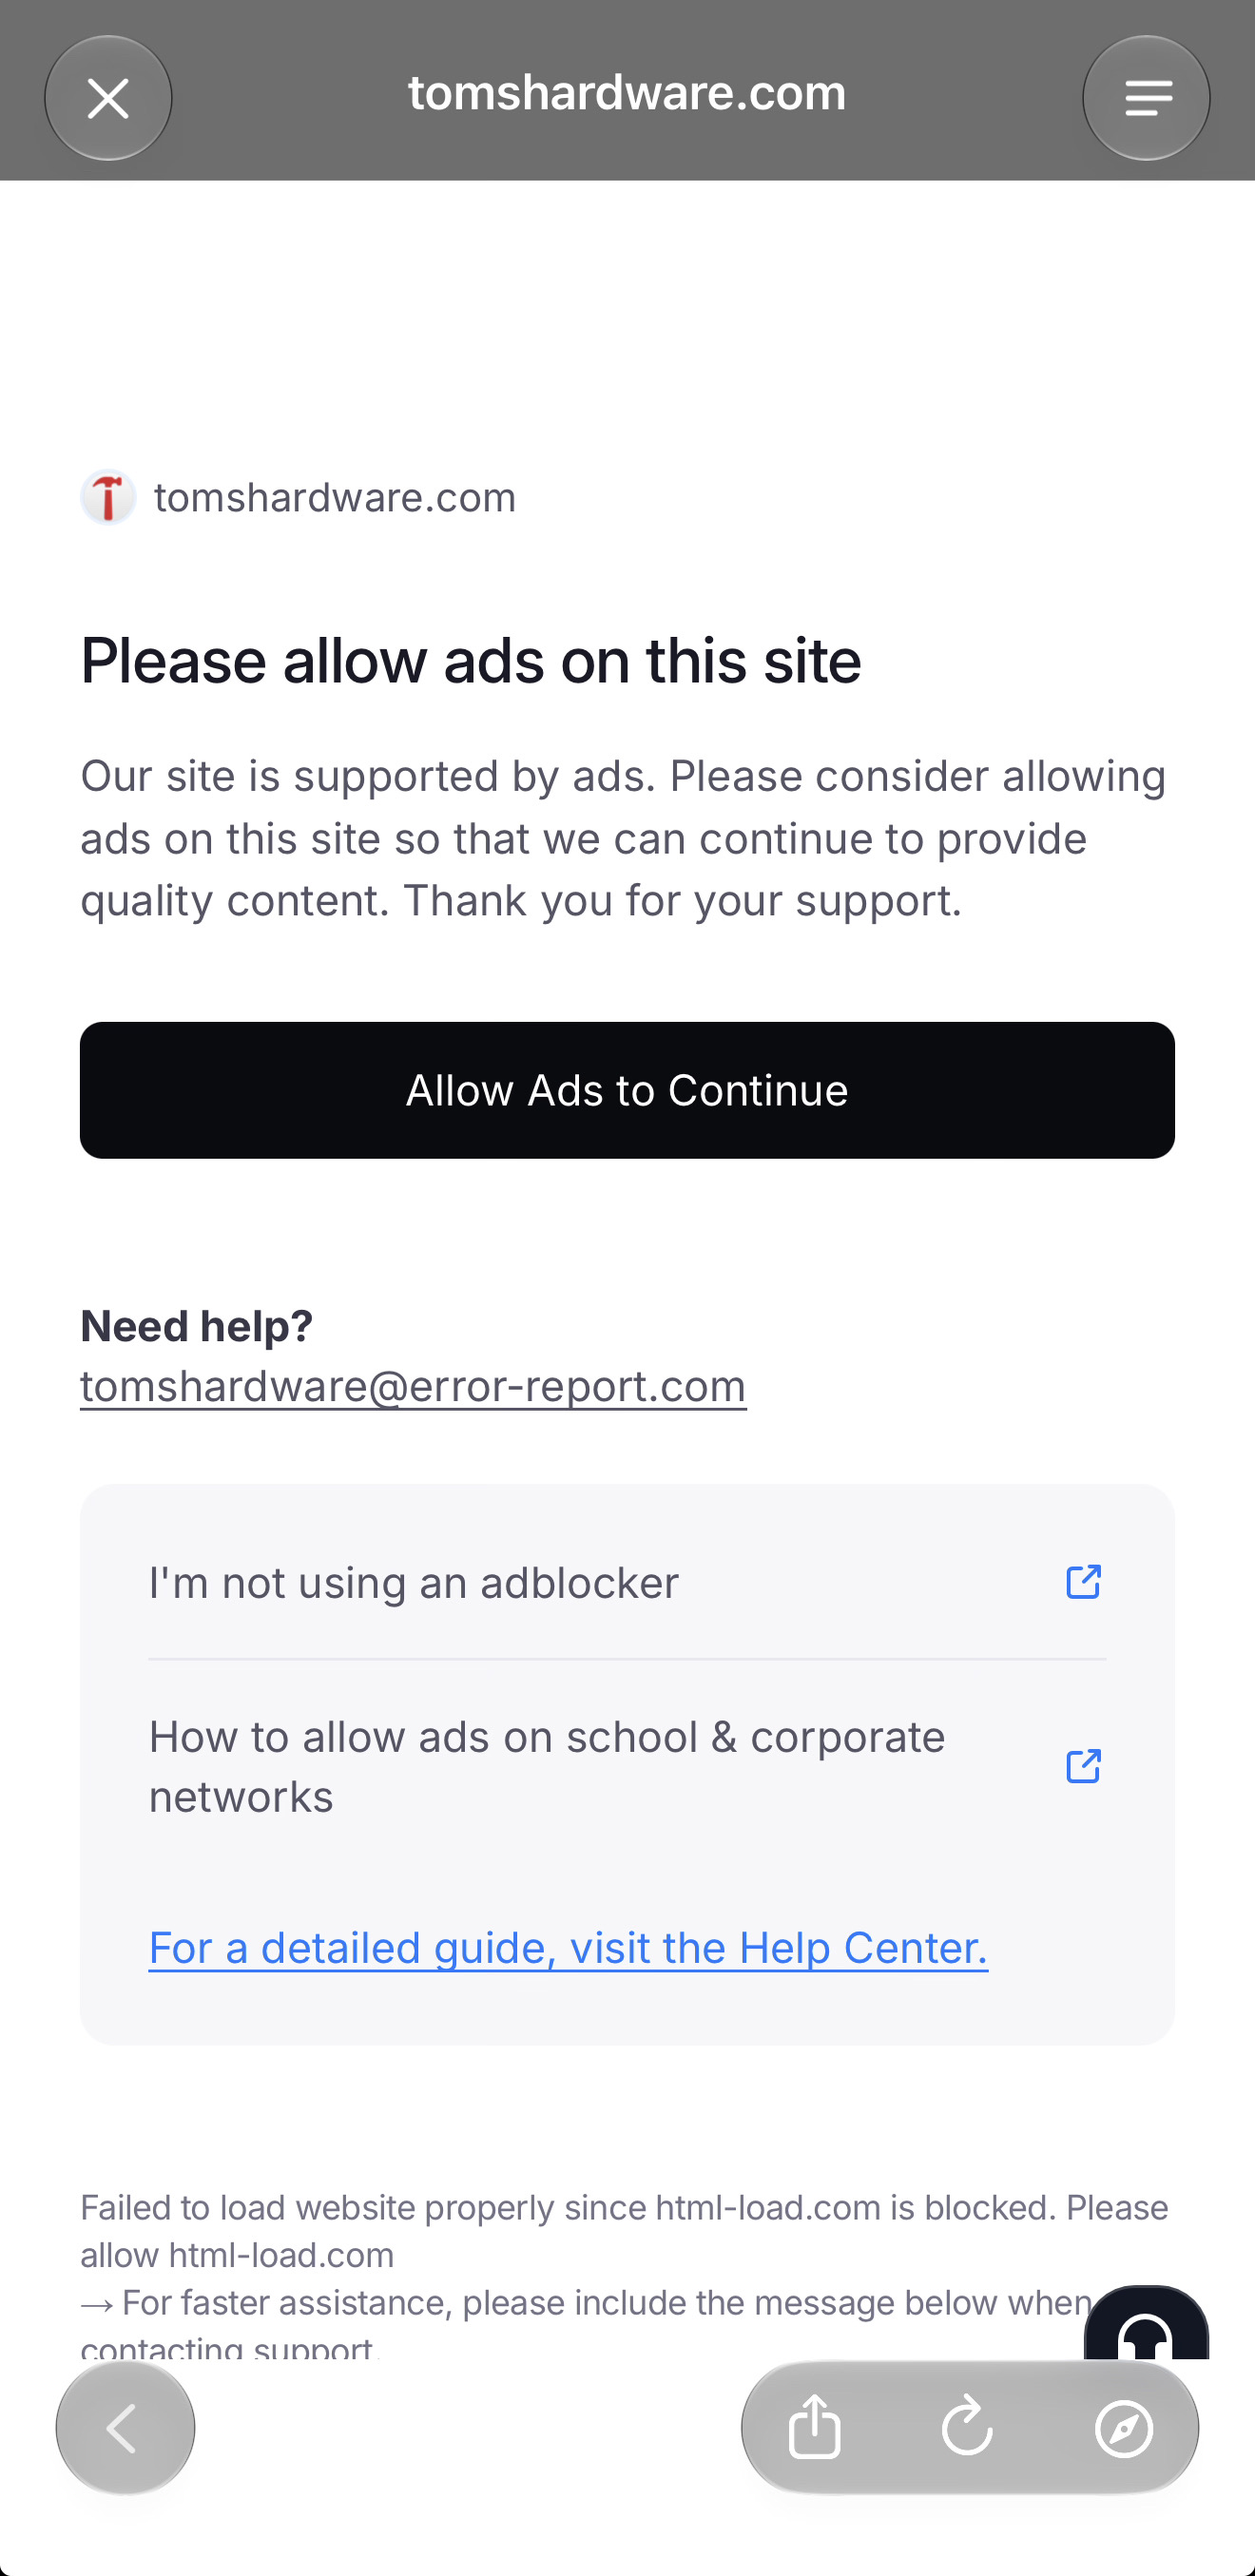
can we PLEASE stop linking stuff from shit-ass sites that use quasi-malware services like Ad-Shield (the service behind the notorious html-load(dot)com, error-report(dot)com etc.)?
These sites intentionally break and block access when a DNS based ad blocker is used. Not because the site can’t load - it actually loads perfectly fine behind the blockout - but because these fuckers intentionally unload CSS to break the site if ads won’t load… via the same exact methods web malware loads malicious scripts.
I have some heavy DNS filtering and the site still loads fine in Vanadium on GrapheneOS. Many sites refuse to load in the way you describe and it is annoying, but I didn’t know this site was doing that.
Interesting.
I run my own AGH gateway at home with pretty heavy filtering, plus my iDevices have a NextDNS profile installed - and now most big tech sites do this crap…
If you use a script blocker (such as UBO) those stupid error pages tend not to work. Not helpful for any unrooted devices, I know, just throwing it out there.
Sadly not an option on iOS.
Sounds to me like you accidentally have a cdn on the list? And can confirm, works for me (but i have usercss for TH anyway; their desktop-layout sucks).
For further information:
html-load(dot)com, error-report(dot)com are domains owned by Ad-Shield and similar “as recovery” services that:
- inject a script into the site from its own host
- script checks if ad blocs load content or not
- if no ad content is loaded, they phone home to html-load(dot)com or a similar address (making it appear to the average user that they’re some “core internet service”)
- id html-load or their other domains aren’t reachable (they send a keyed request so it’s not as easy as having your own server respond with an empty
{}script), the site will unload CSS and deliver a blocking view
No, the block is very specifically about ad recovery via html-load(dot)com…
So it’s a geoip thing? Maybe because GDPR that i don’t get it?
Isn’t there a uB or *monkey script that nips those in the bud? 🤞🏼
Neither of which are available on iOS in non-Safari browsers
Ah, sorry. I had no idea. 😅
Wait wait - is it also advertised as a 1TB card that’s configured to show 1TB of space when you plug it in, but then it’s really just a 4GB card?
it’s really just a 4MB card?
an interim fix using epoxy over the card.
Lmao encase that shit. Bro, we just need more physical security, trust me.
A self destruct could fix it 😆
clearly a feature for when the sd card fails. think of how easy it will be to replace.
Removed by mod
discovered what Li calls backdoor accounts on another maker’s drive, as well as hardcoded keys in other supposedly secure USB storage products.
What i always say; hardware-based encryption is not secure. It’s always in the triangle between speed, security and cost, the vendors go for speed and cost.
And then there’s stuff like this:
but the drive sent the correct password back over USB in plain text for the software to compare, making it easy to capture
Cookie-cutting on the developer side.

